Pentesting shouldn't be a special occasion
With Invicti, you can pentest 10 times more often, keep cost low, and generate findings that are immediately actionable for developers.
AI-powered pentesting needs guardrails to limit noise. Invicti combines intelligent agents with 20+ years of DAST expertise to keep testing focused, control unnecessary cost, and prove what's exploitable.




With Invicti, you can pentest 10 times more often, keep cost low, and generate findings that are immediately actionable for developers.

Invicti agents prepare a plan that incorporates code and technology assessments of your unique apps.

Specialized agents run in parallel, safely using DAST for known exploits and AI logic for complex attack chains.

Every finding is proven exploitable with Invicti runtime intelligence, showing you only critical risks.

Pentest reports are automatically customized to your business context with blended DAST + AI findings.
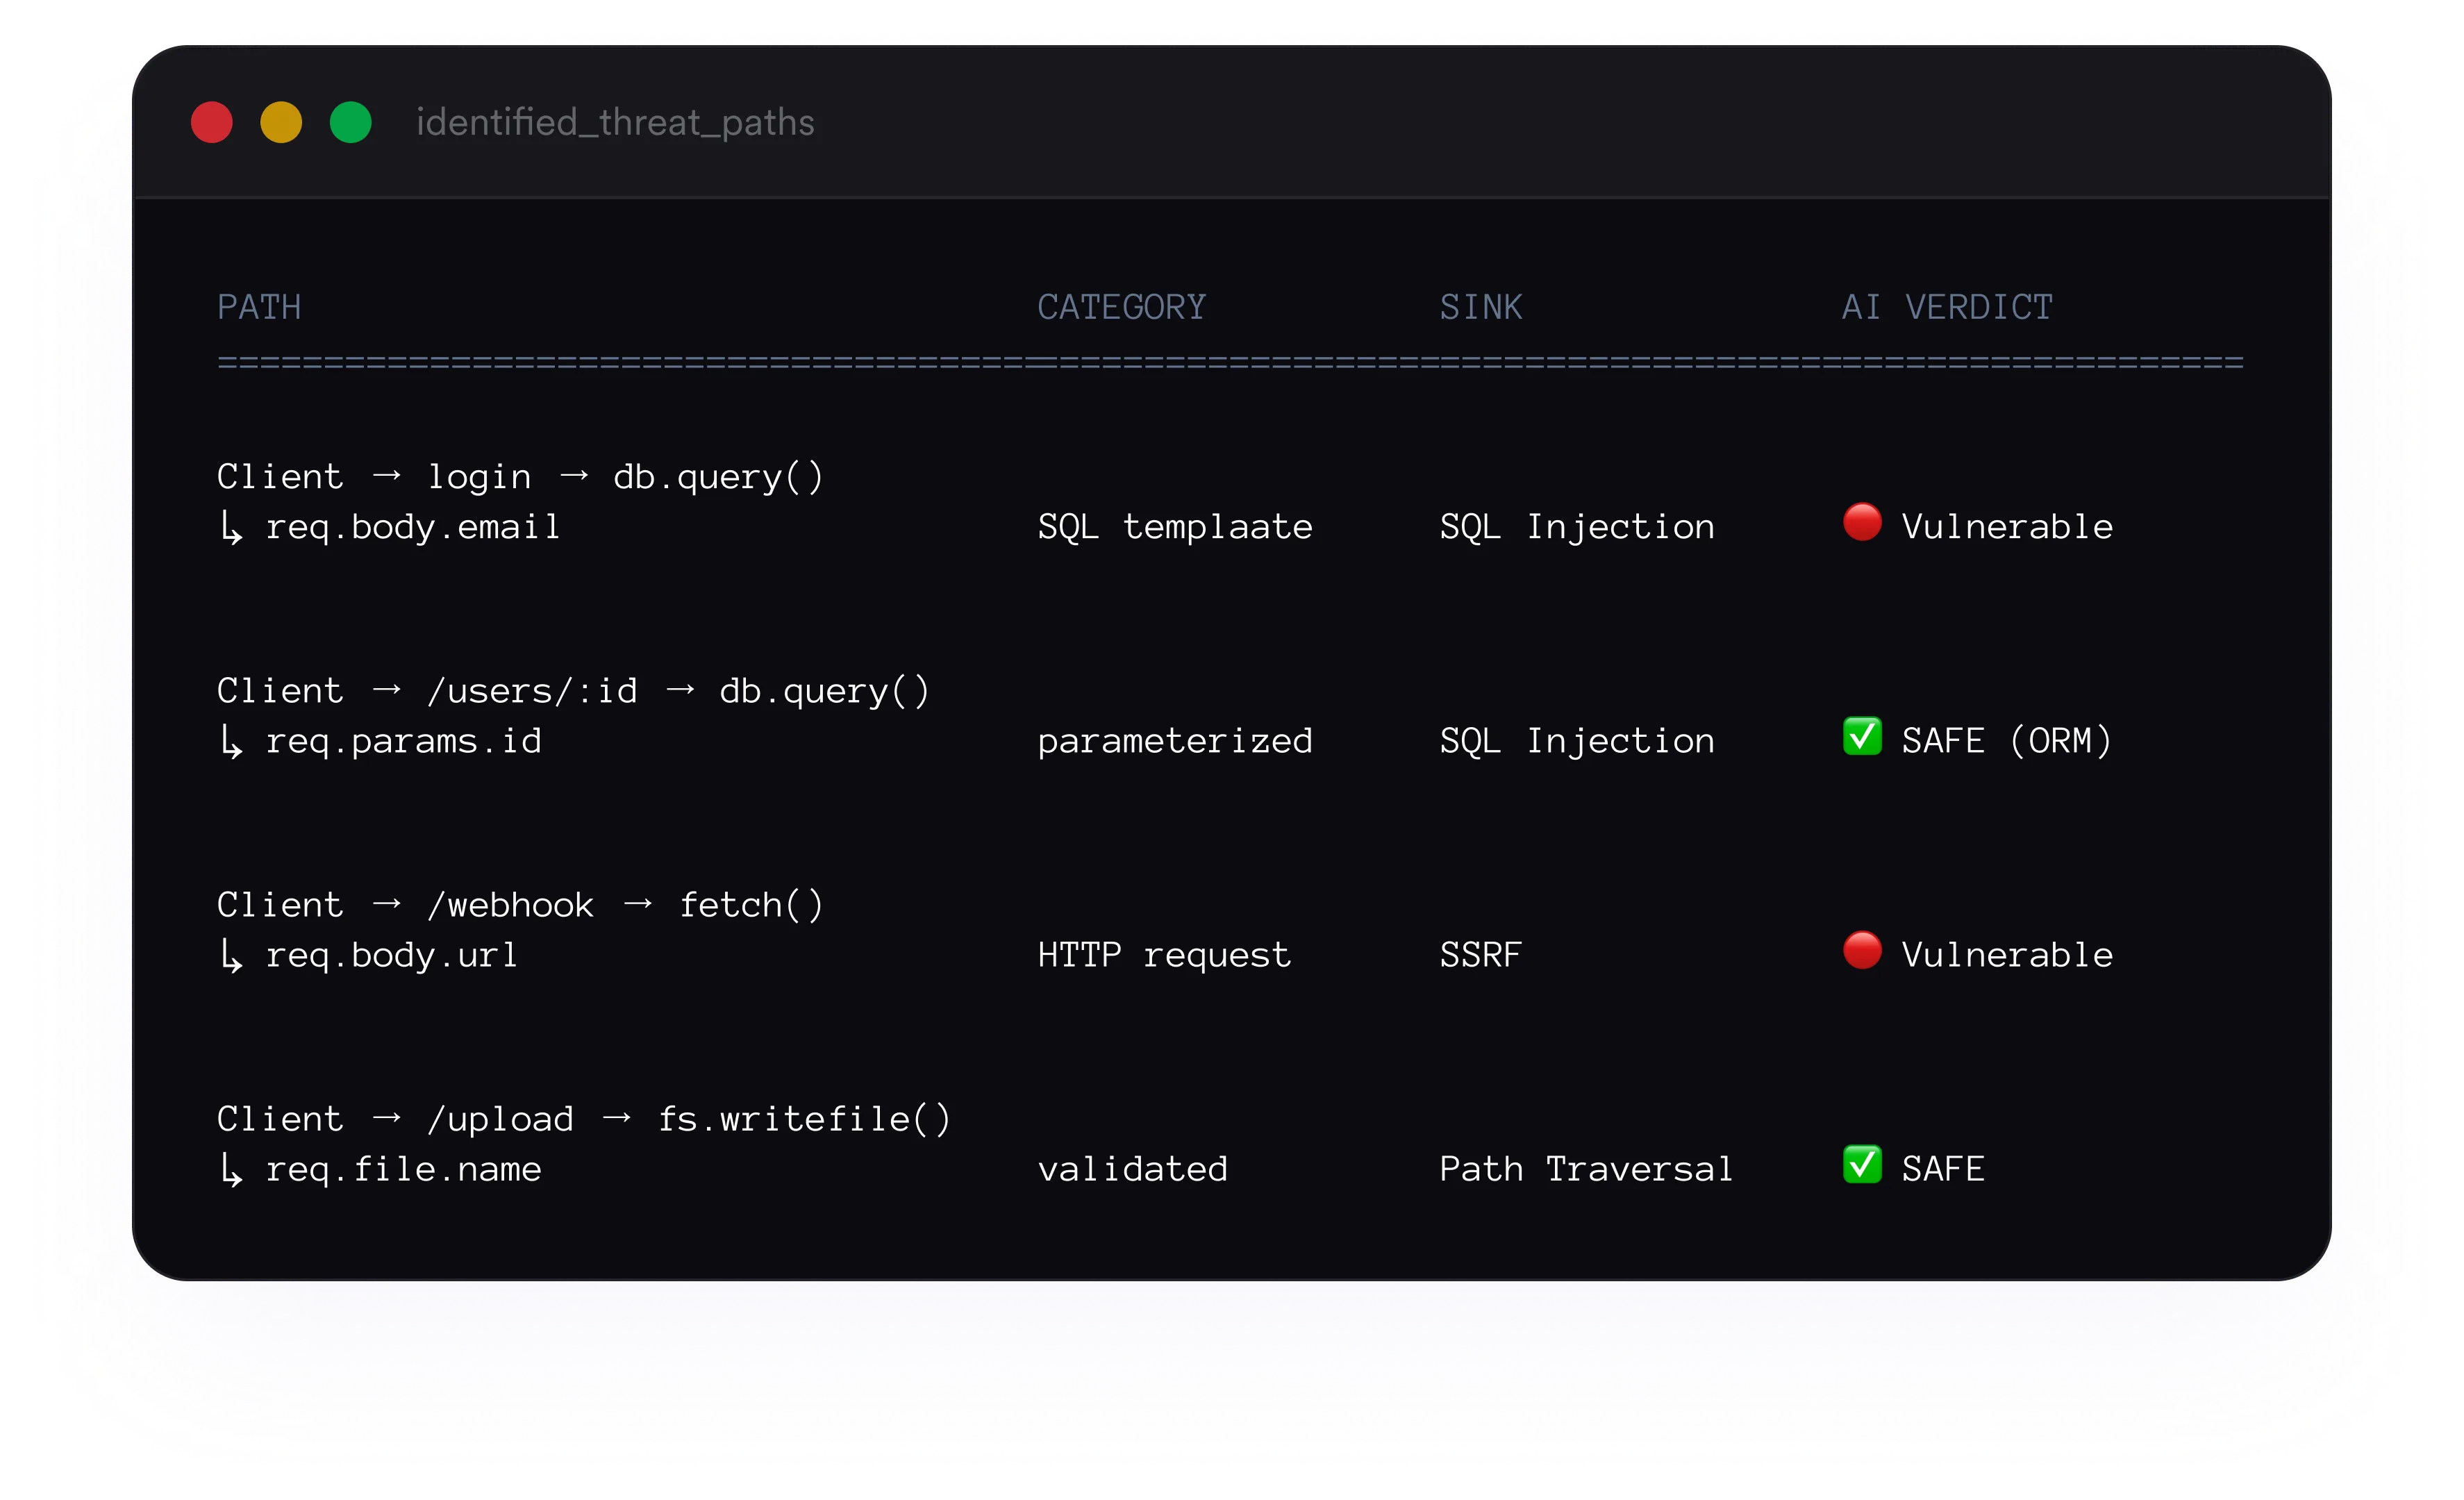
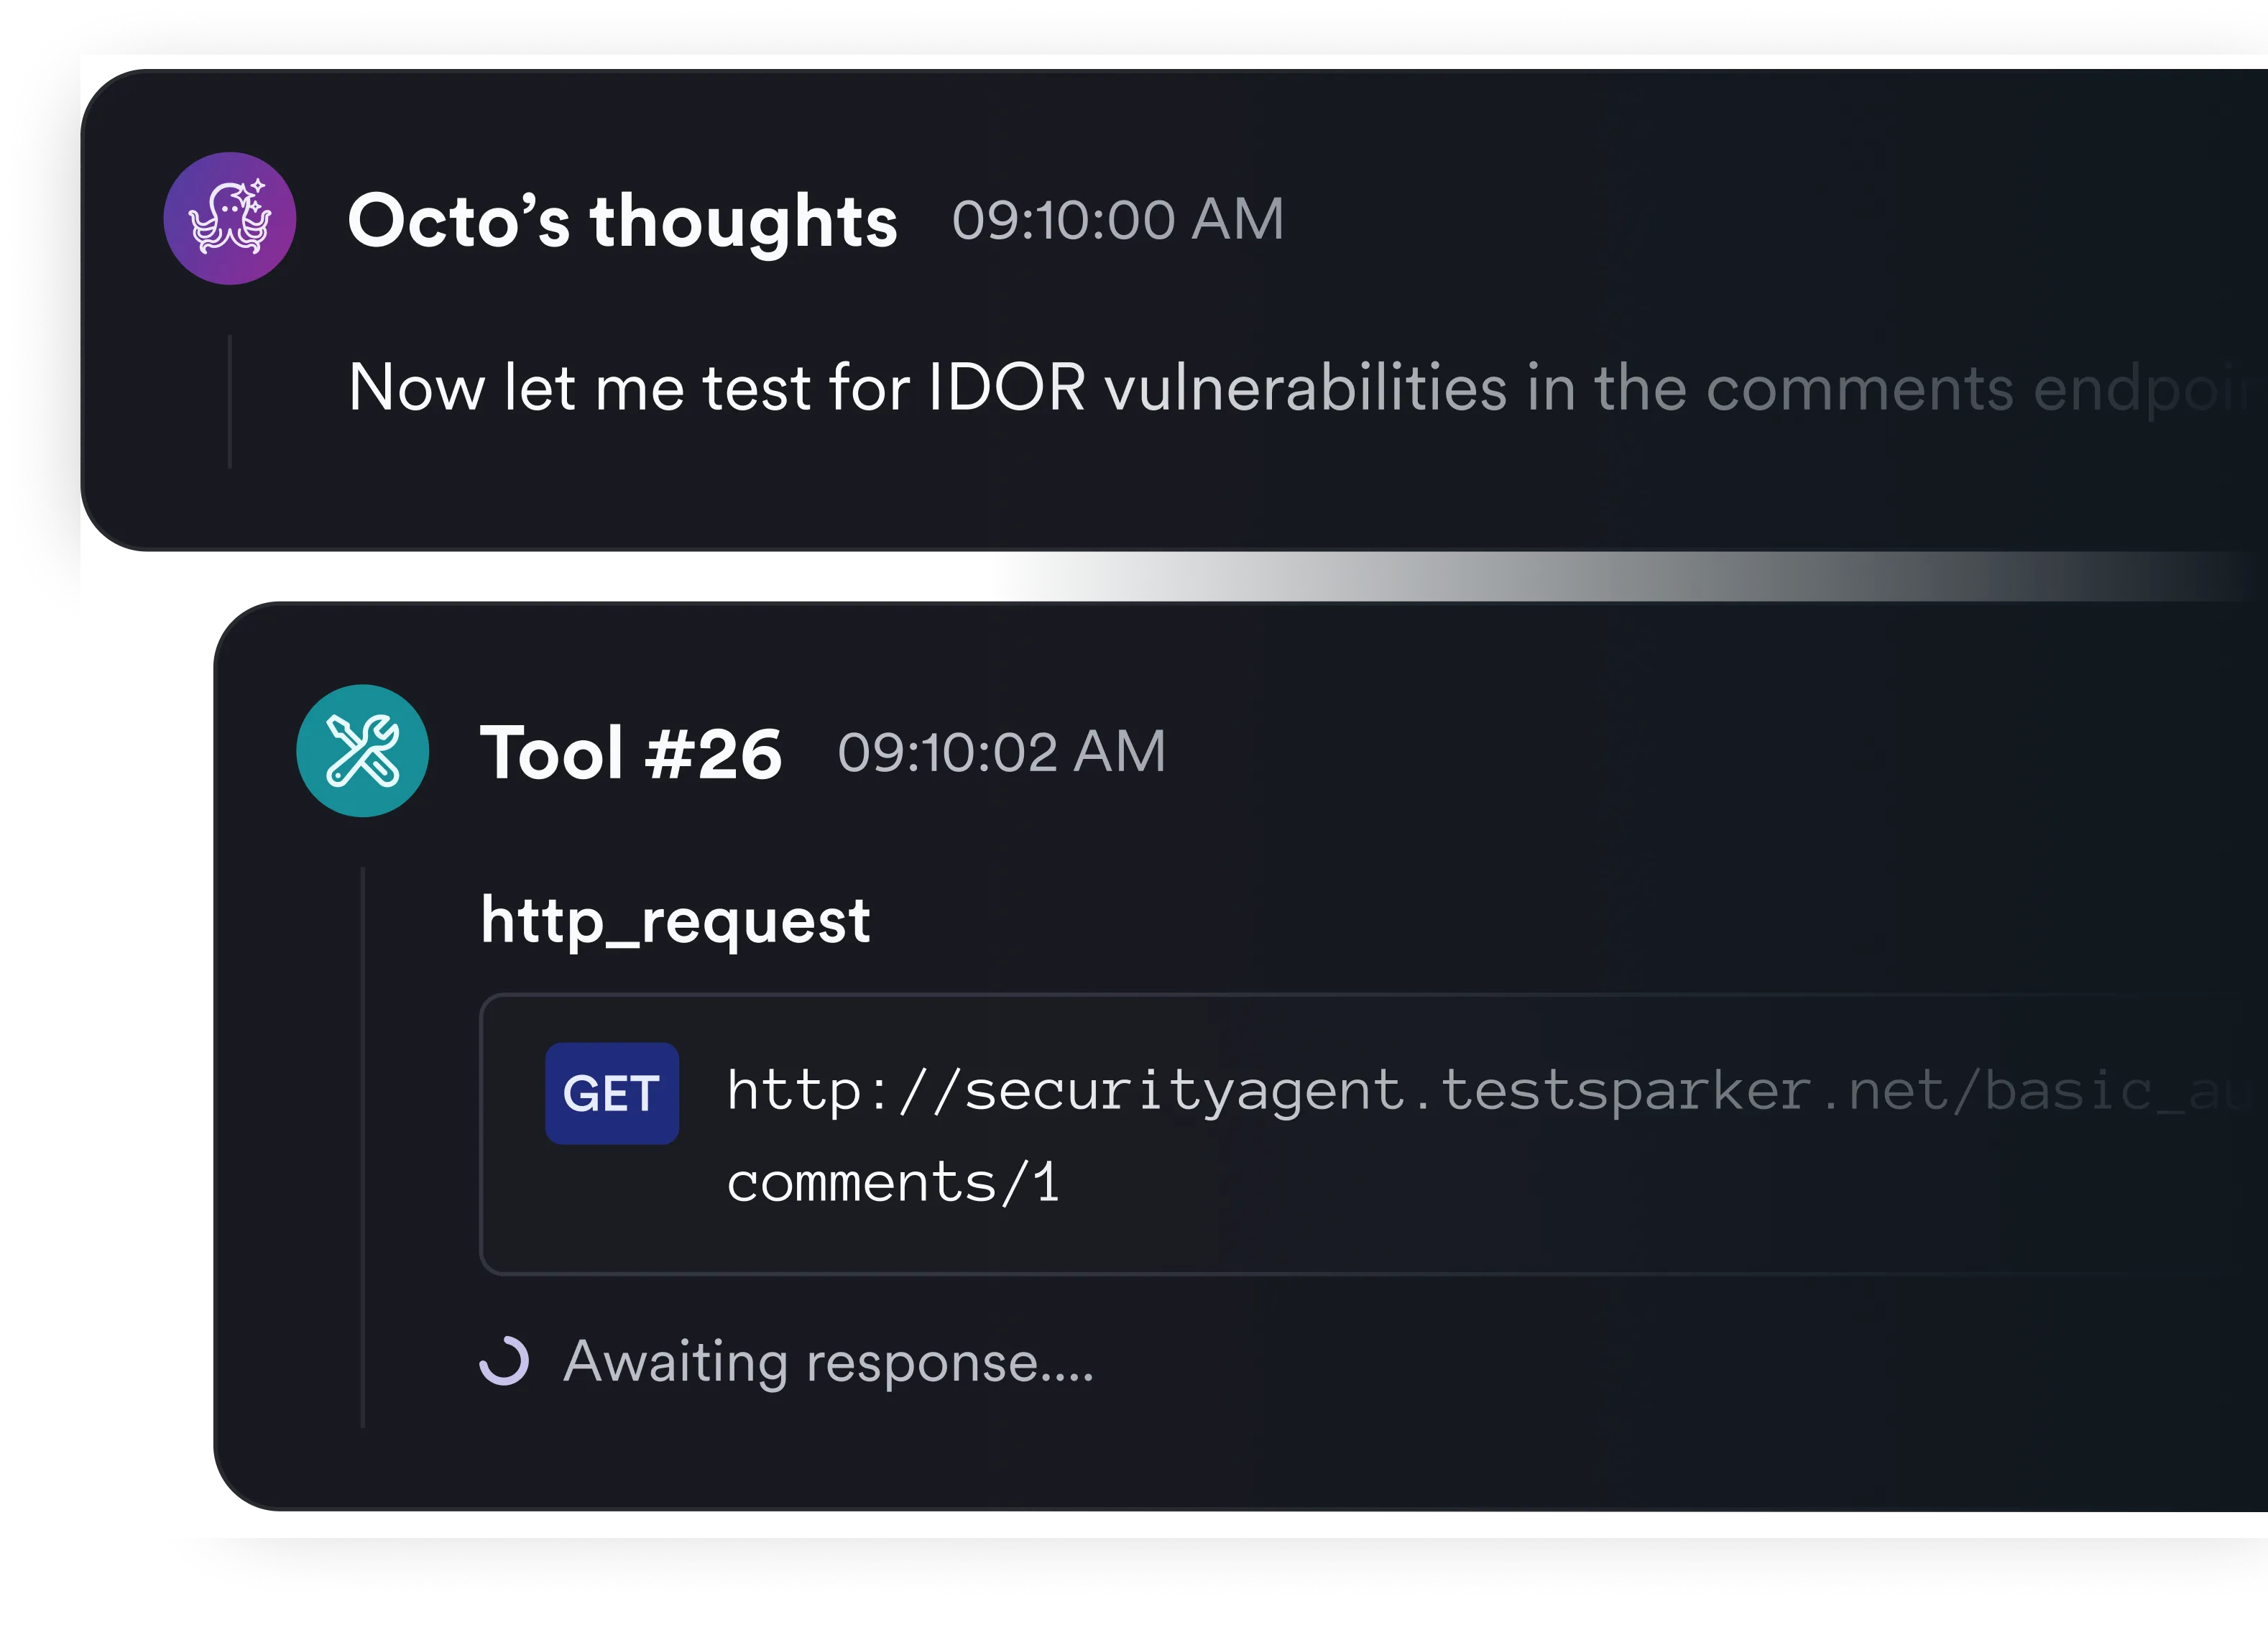
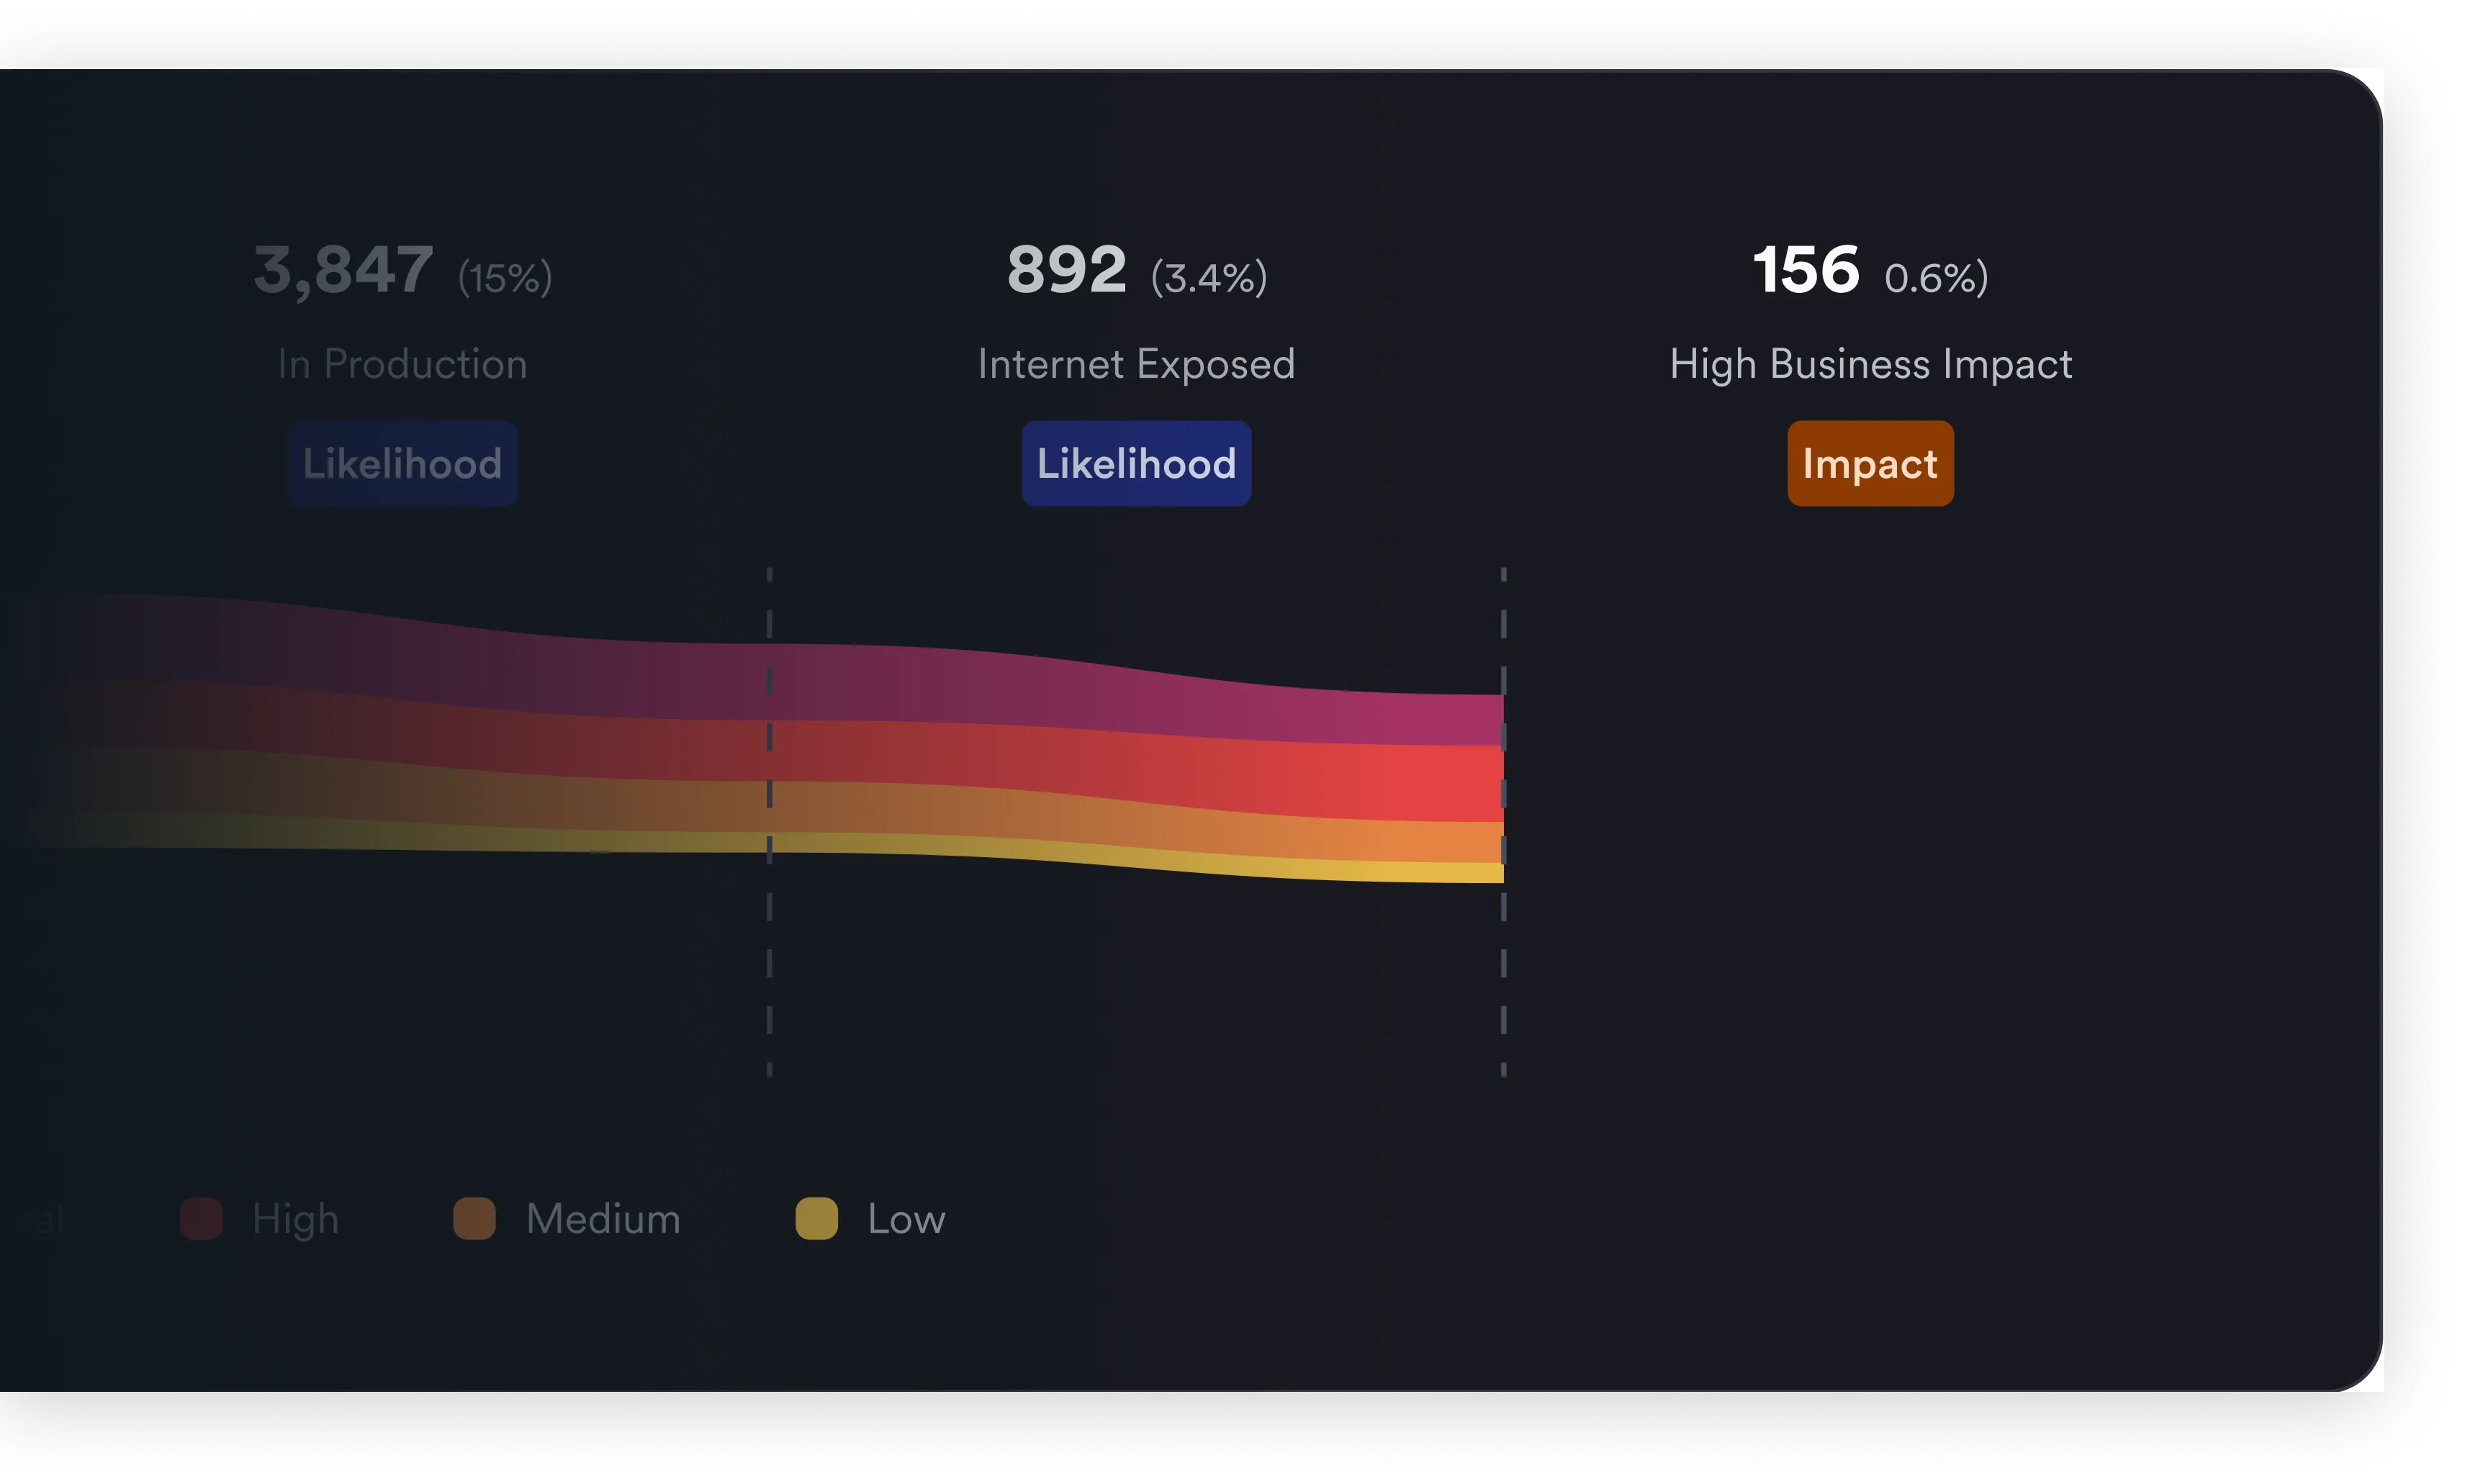

AI agents work with Invicti DAST to minimize token usage and increase efficiency.

Manual pentests can take 4-5 weeks to complete. Invicti achieves the same depth in less than a day.

See the proof of exploit and understand the agentic resoning behind every vulnerability.

Findings are mapped to the OWASP Top 10 and other common frameworks.
“We can fire up Invicti, run the tests as often as we like, and mitigate to our hearts’ content. The budget we were spending every year on penetration testing decreased by approximately 60% almost immediately …

“As opposed to other web application scanners we used, Invicti is very easy to use and does not require a lot of configuring. An out of the…

“Start integrating Invicti into your process and you’ll be surprised at how much time it saves you and how much ‘auto magic’ it brings to your entire development pipeline …

Agentic pentesting uses coordinated AI agents to perform an intelligent penetration test. Instead of running a static ruleset, Invicti creates a tailored attack plan and spins up specialized agents that work in parallel – sharing context and refining attacks like a team of human pentesters.
Agentic pentesting is designed to deliver deeper testing than traditional automated scans, but in a scalable, coordinated way.
While manual pentesting remains valuable for certain compliance requirements, Invicti helps uncover advanced vulnerabilities without the scheduling delays and resource constraints of a one-time manual engagement.
Invicti uses a centralized AI coordinator that spins up focused agents. Each agent specializes in a major vulnerability category such as SQL injection, remote code execution, cross-site scripting, and authentication flaws.
These agents work in parallel and share context with the coordinator and each other to improve the depth and relevance of testing.
DAST can efficiently identify known vulnerability classes at scale.
In Invicti’s hybrid pentesting model, AI agents use that proven engine to execute many of the security checks and focus AI reasoning on uncovering high-value vulnerabilities that deterministic scanning may not easily detect.
Every candidate finding generated is validated using Invicti’s proven confirmation techniques.
Invicti prioritizes zero noise – meaning that vulnerabilities identified by Invicti Agentic Pentest must be confirmed as exploitable before they can appear in your final report.
Yes. The agents can use source code to generate far more detailed results than with black-box testing alone, whether DAST or agentic. When provided, source code allows Invicti to refine attack strategies and generate more targeted security checks tailored to your application.